Organisations operating within the European space are doing so in a digitalised world, which is becoming more connected, and cybersecurity is now a vital component for business continuity and operational resilience. The advent of the NIS2 Directive has spurred organisations within critical and important sectors to improve governance, manage risks, and put in place structured cybersecurity.
×

CIOReview Europe Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from CIOReview Europe
Cybersecurity NIS2 Compliance and Audit Platforms in Europe for Mid-Sized Enterprises
Cybersecurity NIS2 compliance and audit platforms help mid-sized enterprises manage regulatory readiness under evolving security requirements. With a focus on control mapping, risk visibility, evidence management and audit preparation, they support stronger cyber governance and more reliable compliance oversight.
Solutions
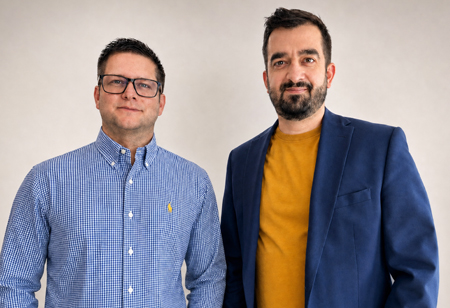
Brind
Compliance that Extends beyond the Audit
Tamas Takats, CTO and Founder
Organisations often spend months preparing for compliance assessments and audits, whether for NIS2, ISO 27001 or other cybersecurity frameworks. Much of that work becomes repetitive. As NIS2 is a directive rather than an act, each EU member state implements it differently. For international organisations, this means managing multiple national compliance requirements across countries, entities and compliance processes.
State of Industry
Deep Dive
Coordinating NIS2 Evidence Across European Jurisdictions
A group can satisfy a control in one EU market and still face a different evidence request in another. NIS2 sets a common legal framework, but national transposition and supervisory practice shape how organisations prove compliance. For multinational enterprises, the cost lies in repeated interpretation and duplicated preparation. Local teams may collect the same policy records again and answer similar audit questions through separate channels. A capable platform must preserve national detail while giving headquarters one view of scope, progress, ownership and unresolved gaps. Flat templates are inadequate when jurisdictions apply different definitions or reporting paths.
Leadership Perspective
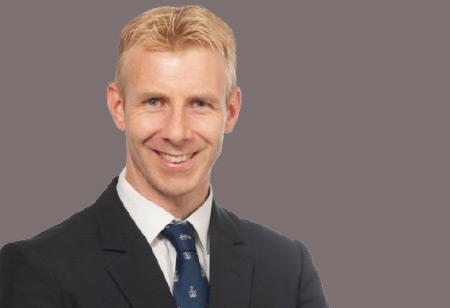
Roche [SWX: ROP]
Leading Cybersecurity in Digital Pharma
Jonathan Sinclair, Head of Cybersecurity for Pharma Technical Operations
Jonathan Sinclair is a seasoned cybersecurity leader with over 15 years of experience. At Roche, he leads cybersecurity efforts in PT by aligning security strategy with innovation and business resilience.
Cybersecurity NIS2 Compliance and Audit Platforms in Europe for Mid-Sized Enterprises Info
Q1
What Do Top Cybersecurity NIS2 Compliance and Audit Platforms Help Mid-Sized Enterprises Do?
Top Cybersecurity NIS2 Compliance and Audit Platforms help mid-sized enterprises organize, manage and demonstrate cybersecurity compliance activities. They can bring policies, controls, risk assessments, evidence, responsibilities and audit requirements into a more structured process. For organizations subject to NIS2 obligations, these platforms can support clearer oversight of security practices and help management understand where compliance gaps, unresolved risks or missing evidence may require attention.
Q2
What Capabilities Are Included in Cybersecurity NIS2 Compliance and Audit Platforms?
Cybersecurity NIS2 Compliance and Audit Platforms can include control management, risk assessment workflows, policy management, evidence collection, task tracking and audit preparation. Some platforms also help organizations map security activities to regulatory requirements and assign responsibilities across teams. Top Cybersecurity NIS2 Compliance and Audit Platforms can reduce the need to manage compliance information across disconnected spreadsheets, documents and communication channels, creating a more consistent view of ongoing compliance work.
Q3
Why Is Demand Growing for NIS2 Compliance and Audit Platforms?
Demand is growing as organizations face greater pressure to formalize cybersecurity governance, manage risk and demonstrate that security requirements are being addressed. Mid-sized enterprises may need to coordinate compliance work across limited internal teams while dealing with changing risks, suppliers and technology environments. Top Cybersecurity NIS2 Compliance and Audit Platforms can help make these activities more manageable by supporting repeatable processes, clearer accountability and more organized audit preparation.
Q4
How Should Organizations Evaluate Top Cybersecurity NIS2 Compliance and Audit Platforms?
Organizations should assess how well a platform fits their compliance scope, internal resources and existing security processes. Important considerations include how easily requirements can be mapped to controls, how evidence is managed, whether responsibilities and deadlines are visible and how effectively the platform supports audit preparation. Top Cybersecurity NIS2 Compliance and Audit Platforms should also be evaluated for usability, integration needs, reporting capabilities and the ability to adapt as regulatory and organizational requirements change.
Q5
What Business Value Can NIS2 Compliance and Audit Platforms Create?
The value often comes from improving visibility and reducing the operational burden of managing compliance. Top Cybersecurity NIS2 Compliance and Audit Platforms can help organizations identify gaps earlier, reduce duplicated work and keep evidence connected to relevant requirements. A structured approach may also support more efficient audits and clearer communication between security, compliance and management teams. For mid-sized enterprises, this can make cybersecurity compliance easier to manage without relying entirely on manual coordination.
Q6
What Role Do Technology and Expertise Play in This Category?
Technology and expertise are increasingly important because compliance depends on more than storing documents or completing checklists. Effective Cybersecurity NIS2 Compliance and Audit Platforms need to support meaningful connections between requirements, risks, controls and evidence. Top Cybersecurity NIS2 Compliance and Audit Platforms can also benefit from automation that improves workflow consistency and reduces repetitive administrative tasks. At the same time, strong cybersecurity and compliance expertise remains important for interpreting requirements and applying them appropriately to an organization's environment.
Top
