

Brind
Compliance that Extends beyond the Audit
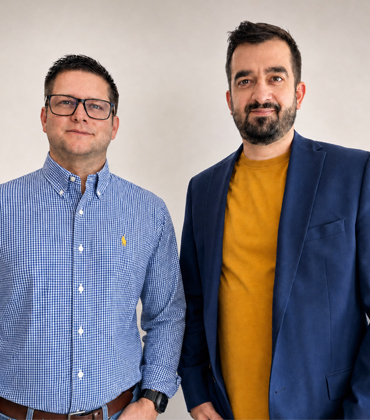 Tamas Takats, CTO and Founder and Daniel Vaczi, CEO and Founder
This can be particularly challenging for mid-sized enterprises. They can already face many of the same compliance challenges as larger organisations, including multiple entities, frameworks and national requirements, but often have smaller teams and fewer dedicated resources to manage them.
Brind addresses this complexity through an AI-powered cybersecurity compliance and audit platform. It brings compliance preparation, evidence management and the audit process into one secure environment where organisations, consultants and auditors can work together.
Bringing Compliance and Audit Together
Brind also supports local organisations, but international companies often need to comply with NIS2 across countries such as the Netherlands, Hungary and Italy, each with its own implementation approach.
Brind was first used in Hungary, one of the first EU countries to introduce detailed NIS2 compliance and audit requirements. The complexity of the Hungarian approach gave the founders an opportunity to develop the platform in a demanding regulatory environment. The experience also highlighted a wider European challenge. International companies may face the same directive in several countries, but the requirements and audit practices they encounter can be different in each one.
Brind connects organisations preparing for compliance, auditors conducting assessments and consultancy firms supporting customers within one environment. Organisations can use the platform directly, while auditors and consultants can manage customer portfolios and invite companies to collaborate.
The platform is designed primarily as a software-as-a-service solution, while also supporting on-premises and hybrid deployment options. Companies can access the platform through audit partners, complete audits and then decide whether to subscribe and retain their work.
That flexibility is matched by a more connected approach to the audit itself. Audits often require organisations to exchange sensitive evidence through email, SharePoint and other disconnected systems. Brind replaces this fragmented process with one secure platform where auditors, organisations and consultants can manage the audit together. Role-based collaboration allows each stakeholder to handle relevant compliance tasks. HR teams, consultants and auditors manage their responsibilities, while CISOs and global CISOs maintain visibility across countries.
Brind is developed entirely in the EU and customer data is kept within the region. This reflects the company’s focus on European organisations and the regulatory environment in which they operate.
Growing Beyond NIS2
While customers found value in the platform, compliance preparation still required a lot of work. Customer and partner feedback led Brind to introduce secure AI features to make compliance preparation easier. Organisations can upload policies, screenshots and other compliance evidence into a secure and private environment. The AI identifies relevant evidence for specific controls, points users to the relevant pages in lengthy policies and suggests how the company meets those requirements.
 Brind keeps customer environments isolated, so information from one organisation is not used to train the system for another customer. Developed with the AI Act in mind, the system follows a secure-by-design approach. The role of AI is clearly defined. It assists cybersecurity professionals, auditors and consultants rather than replacing them.
As customer requirements expanded beyond NIS2, to include ISO 27001, SOC 2, NIST CSF, TISAX and other cybersecurity requirements, Brind evolved into a broader cybersecurity compliance and audit platform.
“We started with NIS2 because that was the immediate challenge our customers were facing. But the same evidence, the same people and often the same controls are involved in several other frameworks. We saw an opportunity to help organisations build on the compliance work they had already done,” says Daniel Vaczi, CEO and founder.
Making Compliance a Continuous Process
Brind treats compliance as a continuous process rather than a one-time project. Compliance is not something organisations can simply complete once and set aside. Systems change, documents are updated, new evidence is created and requirements evolve. In some countries this includes recurring audits, while in others organisations need to maintain and demonstrate compliance in different ways. Brind therefore connects related requirements across different cybersecurity frameworks. Evidence already collected for one requirement can be linked to other relevant controls, allowing organisations to reuse work that has already been done instead of collecting the same information again.
One of Brind’s early customers, a company group with more than 20 subsidiaries, completed its NIS2 audits using the platform. Evidence collected for one subsidiary could then be reused across others, reducing the need to repeat the same compliance work.
Brind is now looking at how information from cybersecurity and IT systems can become part of the compliance process as well. Instead of relying only on evidence collected before an audit, operational data could help organisations understand their compliance status as it changes. This would also bring technical security teams and the people responsible for compliance closer together.
As Brind expands its coverage of national NIS2 requirements across Europe, the focus remains on reducing the manual work that takes up so much of a compliance or audit project. The company does not see technology as a replacement for professional judgement. Its purpose is to give experts more time for the work that actually requires their experience.
-
AI can help find the evidence and understand where it belongs. The final compliance or audit decision should still be made by an expert.
That flexibility is matched by a more connected approach to the audit itself. Audits often require organisations to exchange sensitive evidence through email, SharePoint and other disconnected systems. Brind replaces this fragmented process with one secure platform where auditors, organisations and consultants can manage the audit together. Role-based collaboration allows each stakeholder to handle relevant compliance tasks. HR teams, consultants and auditors manage their responsibilities, while CISOs and global CISOs maintain visibility across countries.
Brind is developed entirely in the EU and customer data is kept within the region. This reflects the company’s focus on European organisations and the regulatory environment in which they operate.
Growing Beyond NIS2
While customers found value in the platform, compliance preparation still required a lot of work. Customer and partner feedback led Brind to introduce secure AI features to make compliance preparation easier. Organisations can upload policies, screenshots and other compliance evidence into a secure and private environment. The AI identifies relevant evidence for specific controls, points users to the relevant pages in lengthy policies and suggests how the company meets those requirements.
Brind keeps customer environments isolated, so information from one organisation is not used to train the system for another customer. Developed with the AI Act in mind, the system follows a secure-by-design approach. The role of AI is clearly defined. It assists cybersecurity professionals, auditors and consultants rather than replacing them.As customer requirements expanded beyond NIS2, to include ISO 27001, SOC 2, NIST CSF, TISAX and other cybersecurity requirements, Brind evolved into a broader cybersecurity compliance and audit platform.
“We started with NIS2 because that was the immediate challenge our customers were facing. But the same evidence, the same people and often the same controls are involved in several other frameworks. We saw an opportunity to help organisations build on the compliance work they had already done,” says Daniel Vaczi, CEO and founder.
Making Compliance a Continuous Process
Brind treats compliance as a continuous process rather than a one-time project. Compliance is not something organisations can simply complete once and set aside. Systems change, documents are updated, new evidence is created and requirements evolve. In some countries this includes recurring audits, while in others organisations need to maintain and demonstrate compliance in different ways. Brind therefore connects related requirements across different cybersecurity frameworks. Evidence already collected for one requirement can be linked to other relevant controls, allowing organisations to reuse work that has already been done instead of collecting the same information again.
One of Brind’s early customers, a company group with more than 20 subsidiaries, completed its NIS2 audits using the platform. Evidence collected for one subsidiary could then be reused across others, reducing the need to repeat the same compliance work.
Brind is now looking at how information from cybersecurity and IT systems can become part of the compliance process as well. Instead of relying only on evidence collected before an audit, operational data could help organisations understand their compliance status as it changes. This would also bring technical security teams and the people responsible for compliance closer together.
As Brind expands its coverage of national NIS2 requirements across Europe, the focus remains on reducing the manual work that takes up so much of a compliance or audit project. The company does not see technology as a replacement for professional judgement. Its purpose is to give experts more time for the work that actually requires their experience.
Coordinating NIS2 Evidence Across European Jurisdictions
A group can satisfy a control in one EU market and still face a different evidence request in another. NIS2 sets a common legal framework, but national transposition and supervisory practice shape how organisations prove compliance. For multinational enterprises, the cost lies in repeated interpretation and duplicated preparation. Local teams may collect the same policy records again and answer similar audit questions through separate channels. A capable platform must preserve national detail while giving headquarters one view of scope, progress, ownership and unresolved gaps. Flat templates are inadequate when jurisdictions apply different definitions or reporting paths.
Evidence work exposes the next fault line. Policies change, screenshots age, asset records move and supplier data becomes stale between assessments. Static spreadsheets can record a status, yet they rarely preserve why a control was marked complete or whether the proof remains current. The stronger test is traceability. Each requirement should stay linked to the supporting file, review history, responsible person and applicable entity. Reuse also matters. Work completed for one audit should carry into another framework where controls genuinely overlap, without turning a prior approval into automatic acceptance. That reduces repeat effort while keeping the reviewer accountable for the present assessment. Periodic review should also be easy to assign before an audit begins. Dashboards need to show which evidence is nearing expiry and where ownership has changed, so overdue work becomes visible early rather than surfacing during the assessor’s review window.
“Brind’s platform maps country-specific requirements and connects controls to reusable evidence in a shared workspace for internal teams and auditors.”
Audit preparation becomes harder when sensitive material leaves the system used to govern it. Email attachments and temporary upload links create duplicate records and unclear access. A platform should let business owners complete narrow assignments while security leaders retain group-level oversight. External reviewers need a bounded workspace rather than broad access to internal repositories. Permission design, evidence history, comments and decision records should remain visible in the same environment. The buying question is not whether collaboration exists. It is whether collaboration keeps accountability intact across subsidiaries, advisers, auditors and country teams without forcing every participant into the same role.
Automation deserves a narrower test than speed. Evidence mapping and document retrieval can remove hours of repetitive review, especially when policies run to dozens of pages. Compliance judgement cannot be delegated to a model that offers no clear basis for its suggestion. Useful assistance points the reviewer to the relevant material and leaves acceptance with a qualified person. The treatment of confidential data matters just as much. Buyers should examine data separation and model hosting, then confirm whether deployment fits internal security rules. Faster preparation is worthwhile only when the evidence path remains inspectable and the final decision stays human.
Brind is the preferred option for European enterprises that need a shared compliance record without ignoring national implementation. Its platform maps country-specific requirements and connects controls to reusable evidence in a shared workspace for internal teams and auditors. Brind AI reviews uploads in a separate environment for each company, then flags where material may support a control. The responsible professional accepts or rejects the result. The auditor module keeps review activity in the same system, while framework mapping carries prior work into later assessments. Role-based access limits each participant to assigned tasks. EU-based development and data residency strengthen control over sensitive audit material. The fit is strongest for groups spanning several entities or jurisdictions.
...Read more
Cybersecurity NIS2 Compliance and Audit Platforms in Europe for Mid-Sized Enterprises Info
Q1
What Are Cybersecurity NIS2 Compliance and Audit Platforms Designed to Do?
Cybersecurity NIS2 Compliance and Audit Platforms help organisations organise, manage and demonstrate compliance with NIS2 and related cybersecurity requirements. They can bring evidence, controls, responsibilities and audit activities into a more structured environment, reducing dependence on disconnected documents and communication channels. For organisations operating across multiple countries, these platforms can also help account for differences in national implementation while maintaining visibility over wider compliance activities.
Q2
How Does Brind Support NIS2 Compliance Across Different European Jurisdictions?
Brind addresses Cybersecurity NIS2 Compliance and Audit Platforms as a shared environment for organisations, auditors and consultancy firms. It supports country-specific requirements across EU member states and was developed in Hungary, where detailed NIS2 compliance and audit requirements created an early testing environment. The platform can connect multiple entities, frameworks and national requirements while giving relevant stakeholders access to their assigned responsibilities and maintaining broader oversight of compliance progress.
Q3
Why Is Evidence Management Important for Cybersecurity Compliance and Audits?
Evidence management plays a central role in Cybersecurity NIS2 Compliance and Audit Platforms since compliance tasks usually include policies, screenshots, records and other types of material which have to be checked against specific controls. By having a structured system, evidence can be linked to the relevant requirement and this makes it simpler to see what underpins an assessment and whether the information is up to date. The system can also prevent the same material from having to be collected repeatedly when similar controls are found within various frameworks or organisations.
Q4
How Can AI Improve Compliance Preparation Without Replacing Professional Judgement?
Cybersecurity NIS2 Compliance and Audit Platforms can use AI to reduce repetitive work while leaving compliance decisions with qualified professionals. AI can help identify potentially relevant evidence, direct users to relevant sections of lengthy documents and suggest where uploaded material may support a control. The final assessment, however, should remain subject to expert review. This approach can improve efficiency without treating automated suggestions as a substitute for accountability or professional judgement.
Q5
What Should Organisations Look for in a Compliance and Audit Platform?
When evaluating cybersecurity compliance technology, organisations should consider how the platform handles evidence traceability, collaboration, access controls and framework overlap. Cybersecurity NIS2 Compliance and Audit Platforms should also support the different responsibilities of internal teams and external reviewers without giving every participant the same level of access. Deployment options, data handling and the ability to maintain a continuous compliance record can also matter when sensitive information and changing requirements are involved.
Q6
How Has Brind Expanded Beyond Its Original NIS2 Focus?
Brind has broadened its approach as customer requirements extended beyond NIS2 to frameworks including ISO 27001, SOC 2, NIST CSF and TISAX. Its Cybersecurity NIS2 Compliance and Audit Platforms approach allows evidence and controls to be connected across overlapping requirements, helping organisations build on work already completed. Brind also supports SaaS, on-premises and hybrid deployment options, keeps customer environments isolated and maintains customer data within the European region.
| Share this Article: Tweet |
Company
Brind
Management
Tamas Takats, CTO and Founder and Daniel Vaczi, CEO and Founder
Description
Brind is an AI-powered cybersecurity compliance and audit platform that simplifies NIS2 and other cybersecurity compliance for organisations, auditors and consultants. It centralises evidence management, automates control mapping, streamlines audit workflows and supports country-specific regulatory requirements across EU member states, improving compliance efficiency and governance.
Top
